
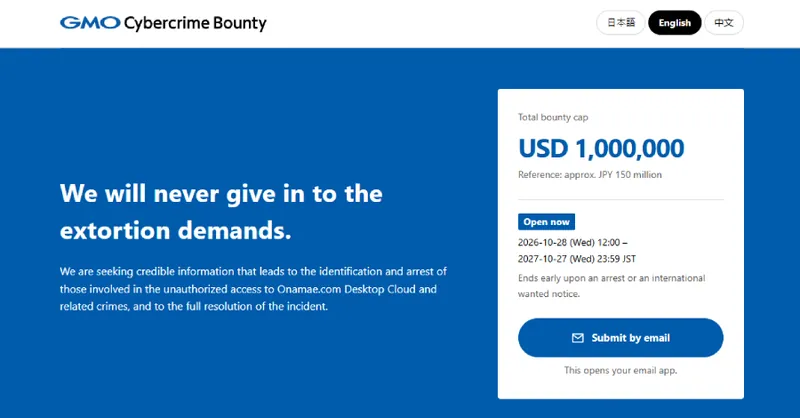
GMO Launches $1 Million Bounty After FX Cloud Breach
GMO Internet Group announced a bounty program offering up to $1 million for tips that lead to the arrest of attackers who breached its Onamae.com Desktop Cloud service. The program began on October 28, 2026 and will close on October 27, 2027, unless an arrest or an international wanted notice is issued sooner.
Attack Path and Exposure
The attackers accessed Windows desktops provisioned by the Onamae.com Desktop Cloud service. These desktops are used by clients for foreign-exchange (FX) trading. After compromising the service, the attackers extracted customer credentials and used them to place unauthorized trades on some customers’ accounts. The broker linked these trades to logins that had been leaked from the cloud service.
On October 21, the attackers demanded approximately $50 million (about ¥8 billion) from GMO, citing the breach. They also threatened customers’ trading accounts and data. The attackers posted material on their website on October 27 that they claimed contained information about GMO and its customers. GMO shut down the attackers’ domain and its mirrors at about 4 a.m. Japan time on October 28.
Bounty Program Mechanics
Tips are submitted via email to a dedicated address listed on GMO’s bounty website. The program accepts tips in Japanese, English, or Chinese and allows anonymous submissions. GMO will pay only if a tip leads to an arrest—by Japanese police or abroad—or to an international wanted notice such as an Interpol Red Notice. GMO determines the payout amount based on the tip’s contribution to the investigation. A single tipster can receive the full $1 million, or the total can be split among multiple tipsters.
Tipsters must prove their identity before payment. GMO disallows tips that involve breaking into systems, negotiating with attackers, or sending leaked data, credentials, or malware. Tips are shared with Japanese authorities and, when appropriate, with foreign law-enforcement agencies.
Defensive Actions for Cloud Operators
- Validate Isolation – Verify that the cloud environment isolates customer desktops from each other and from the underlying host. Ensure that a compromise of one desktop does not grant lateral movement to others.
- Credential Management – Enforce multi-factor authentication for all administrative and trading accounts. Rotate credentials regularly and monitor for reuse across services.
- Audit Logging – Enable comprehensive logging on all Windows desktops, including login events, process creation, and network connections. Store logs in a tamper-evident repository.
- Network Segmentation – Restrict outbound traffic from customer desktops to only the necessary trading endpoints. Apply firewall rules that block unexpected ports and protocols.
- Incident Response Readiness – Prepare an incident-response playbook that includes steps for isolating compromised desktops, preserving evidence, and coordinating with law-enforcement.
- Threat Intelligence Sharing – Participate in threat-intel feeds that track credential-reuse attacks and FX-trading-related fraud.
What to Watch Next
- Attribution Progress – GMO’s bounty program may accelerate the identification of the threat actors. Monitor public statements from Japanese police and Interpol for updates.
- Credential Leak Sources – Investigate whether the leaked credentials originated from a known data-breach database or from a targeted phishing campaign.
- Regulatory Impact – The breach involves financial trading. Regulatory bodies may issue guidance on cloud security for FX platforms.
- Customer Impact – Clients who experienced unauthorized trades should verify account balances and report any discrepancies to their brokers.
FAQ Snippets
What service was breached?
The Onamae.com Desktop Cloud service that hosts Windows desktops for FX trading.
How much is the bounty?
Up to $1 million, payable only if a tip leads to an arrest or an international wanted notice.
When does the bounty program end?
October 27, 2027, or earlier if an arrest or wanted notice is issued.
What evidence is required for a tip to be paid?
Information linking attackers, servers, domains, IPs, accounts, or cryptocurrency addresses to the attack, with evidence of how the crimes were carried out.
What defensive steps should cloud operators take?
Validate isolation, enforce MFA, enable audit logging, segment networks, prepare incident-response playbooks, and share threat intelligence.
Technical Reference
For a broader view of cloud-related vulnerabilities, see the Zero-Day Vulnerability & CVE Exploit Matrix.
Related coverage
- FortiBleed 2.0 Exposes 40,573 Secrets, PHP2Shell Scanning Continues, and 26 Other Threats Detected
- Yoba Crypto Miner Campaign Uses Signed AI Binaries to Deploy Malicious DLLs