
PHP Releases Second Windows Update in Five Days to Patch PHP Brotli Flaw
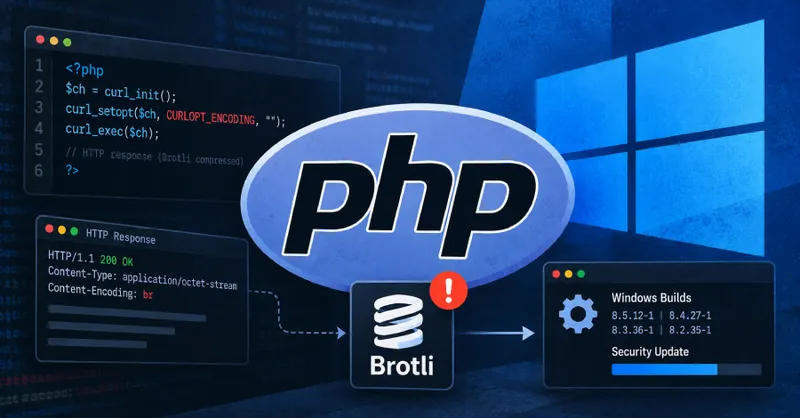
PHP released a second Windows update within five days to patch the PHP Brotli flaw (CVE-2026-111497). The flaw resides in Brotli 1.2.0, the compression library bundled with PHP Windows builds. An attacker can trigger memory corruption and potentially execute code by sending a crafted HTTP response that the cURL extension decompresses automatically.
Affected Builds and Fix Scope
The rebuilt packages—8.5.12-1, 8.4.27-1, 8.3.36-1, and 8.2.35-1—replace Brotli 1.2.0 with 1.2.1. The PHP core code remains unchanged, so the API surface is identical to the previous releases. Each package includes a bill of materials that lists Brotli 1.2.0 as the vulnerable component in the prior builds. The only difference visible to users is the suffix “-1” in the file name and the updated SHA-256 hash.
Attack Vector: cURL Automatic Decompression
The vulnerability activates when the cURL extension decompresses HTTP responses automatically. By default, cURL disables automatic decompression, but applications can enable it by setting CURLOPT_ENCODING. An empty string value tells cURL to accept all supported encodings, including Brotli. Guzzle, a widely used PHP HTTP client, sets CURLOPT_ENCODING to an empty string by default in releases 7.16.1 and 8.3.1. An application that uses Guzzle without changing this default will satisfy the conditions that allow the flaw to be triggered on the affected Windows builds.
Mitigation Guidance
PHP recommends that Windows users download the new builds from the official PHP website. Because the PHP version number does not change, the output of php -v remains the same before and after the update. The file name suffix and the SHA-256 hash on the downloads page identify the patched package.
Defenders should:
- Verify that the installed PHP binaries match the SHA-256 hashes listed on the PHP downloads page.
- Audit application code that uses cURL or Guzzle to confirm whether automatic decompression is enabled.
- If automatic decompression is required, consider patching the application to use a hardened Brotli library or disabling the vulnerable feature until a later update.
Operational Impact
The update does not alter PHP’s API or runtime behavior beyond the library replacement. Existing applications should continue to run without modification. However, deployments that rely on automatic decompression via cURL or Guzzle may be exposed to memory corruption if the vulnerable Brotli version is present.
Next Steps for Operators
- Download the latest Windows packages from the PHP website and replace the existing binaries.
- Re-run any automated deployment scripts to ensure the new binaries are used.
- Monitor application logs for anomalous memory usage or crashes that could indicate exploitation attempts.
Implications for Cloud and Identity Services
Cloud platforms that host PHP applications on Windows containers or virtual machines must ensure that the underlying image includes the patched Brotli library. Identity services that expose HTTP endpoints to external clients should verify that their HTTP client libraries do not enable automatic decompression unless absolutely necessary. Failure to update can expose the service to remote code execution that could compromise user identities.
What to Watch Next
- PHP’s rapid release cadence suggests that additional memory-corruption issues may surface in bundled libraries. Operators should monitor the PHP security advisory feed for new CVEs.
- The PHP community may release a hardened Brotli library that removes the automatic decompression path. Deploying such a library would eliminate the attack surface.
- Cloud providers may issue platform-level patches that replace the vulnerable Brotli library in their managed PHP images.
The rapid release cadence—two updates within five days—highlights PHP’s responsiveness to emerging memory-corruption risks in bundled libraries.
Zero-Day Vulnerability & CVE Exploit Matrix
Related coverage
- PHP2Shell RCE Exposes Web Apps – Immediate Patch Required
- PHP CVE-2026-109618 Trigger Widespread Site Outages