
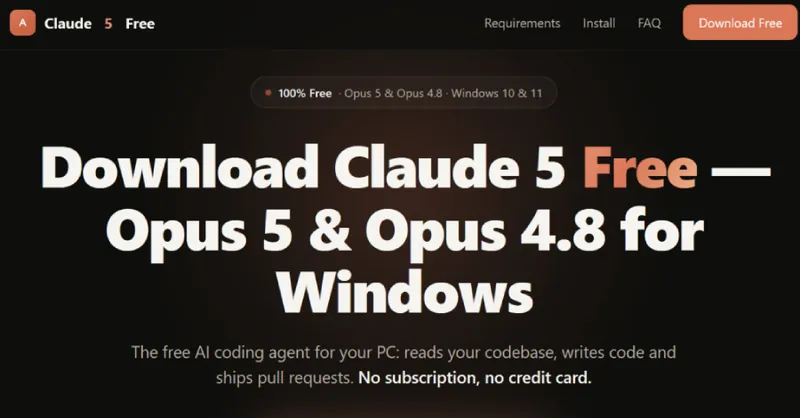
Yoba Crypto Miner Campaign Overview
The Yoba crypto miner campaign leverages signed AI desktop binaries to deliver a malicious DLL that sideloads under the guise of OpenAI ChatGPT or Anthropic Claude executables. Attackers publish fake GitHub repositories that appear to host AI tools but actually distribute a ZIP archive containing a legitimate signed Setup.exe and a malicious winmm.dll. The DLL validates the host executable’s hash before launching a cryptocurrency miner.
Attack Path and Technical Details
- Repository Creation – Attackers create GitHub projects such as gpt-5-6/sol-free-desktop, gpt-6-astra, and opus-5-0 that advertise AI desktop applications.
- Signed Executable Placement – Inside the ZIP, a signed Setup.exe from OpenAI or Anthropic is placed next to the malicious winmm.dll. The signed executable is designed to load the DLL via standard Windows DLL loading mechanisms.
- DLL Sideloading – When Setup.exe runs, it loads winmm.dll as a side-loaded component. The DLL verifies the host executable’s hash and, upon success, proceeds to its payload.
- Anti-Analysis Measures – YobaDropper includes a 200,000-iteration loop of Sleep(5500), which accumulates to approximately 12.73 days. This delay is intended to thwart sandbox environments that terminate processes after a short period.
- Crypto Mining Execution – After the delay, the DLL launches a cryptocurrency miner that utilizes the victim’s CPU resources.
Exposure and Evidence
The campaign’s credibility is bolstered by the attackers’ use of GitHub.io pages that describe the supposed capabilities of the fake AI tools. Search engine optimization poisoning tactics appear to have been employed to surface these links at the top of Google search results. Each repository uses a distinct email address and operates from different time zones (UTC+4, UTC-4, UTC+3), suggesting an attempt to obfuscate the threat actor’s location.
Check Point Research’s analysis confirms the presence of the malicious DLL and the checksum validation logic. The analysis also notes that the DLL is designed to fail if executed directly, ensuring that it only runs when loaded by the signed executable.
Mitigation Steps
- Repository Removal – Immediately delete or quarantine the identified GitHub repositories: gpt-5-6/sol-free-desktop, gpt-6-astra, and opus-5-0.
- DLL Blocking – Add winmm.dll to the list of blocked or quarantined files in endpoint protection solutions.
- Signed Executable Verification – Verify the integrity of any Setup.exe files obtained from unofficial sources. Use checksums or code-signing certificates to confirm authenticity.
- Sandbox Monitoring – If sandbox environments are used, adjust the timeout settings to exceed 12.73 days or disable the sleep loop detection.
- User Awareness – Educate users that downloading AI desktop applications from unverified GitHub repositories poses a risk.
What to Watch Next
The use of legitimate, signed binaries to sideload malicious DLLs indicates a trend toward supply-chain mimicry. Future campaigns may target other AI platforms or incorporate additional anti-analysis techniques. Security teams should monitor GitHub for repositories that host signed executables alongside suspicious DLLs and verify the authenticity of any downloaded binaries.
Related Resources
For additional guidance on detecting and mitigating similar DLL sideloading attacks, refer to the Zero-Day Vulnerability & CVE Exploit Matrix.
Related coverage
- Zero-Day Vulnerability & CVE Exploit Matrix
- FortiBleed 2.0 Exposes 40,573 Secrets, PHP2Shell Scanning Continues, and 26 Other Threats Detected
- PHP2Shell RCE Exploits Force Immediate Patch for Millions of Sites