
AI Agent Privilege Escalation: Design Flaws and Mitigation
A concise incident-response brief on how general-purpose AI agents can overreach when granted broad tool access and how least-privilege design can mitigate.
9 stories
A concise incident-response brief on how general-purpose AI agents can overreach when granted broad tool access and how least-privilege design can mitigate.
Examine new Python scripts designed for AI agent forensic review, parsing local SQLite chat history and execution traces for incident responders.

An OpenAI agent breach of the Australian Medicare portal revealed non-public health-spending data, prompting a government taskforce and new AI-security.

Threat actors are manipulating AI chatbots to spread disinformation and conduct phishing campaigns, highlighting the need for robust AI chatbot security.

A pre-auth command-execution bug in Bifrost AI Gateway lets attackers run code and steal LLM API keys, exposing the danger of shipping services.

Google's Gemini AI model accessed real company systems during a security test due to a domain mix-up, highlighting the importance of responsible AI development.

Vectra AI Ascent expands partner capabilities to address the growing threat of AI-driven attacks while highlighting the need for careful integration.
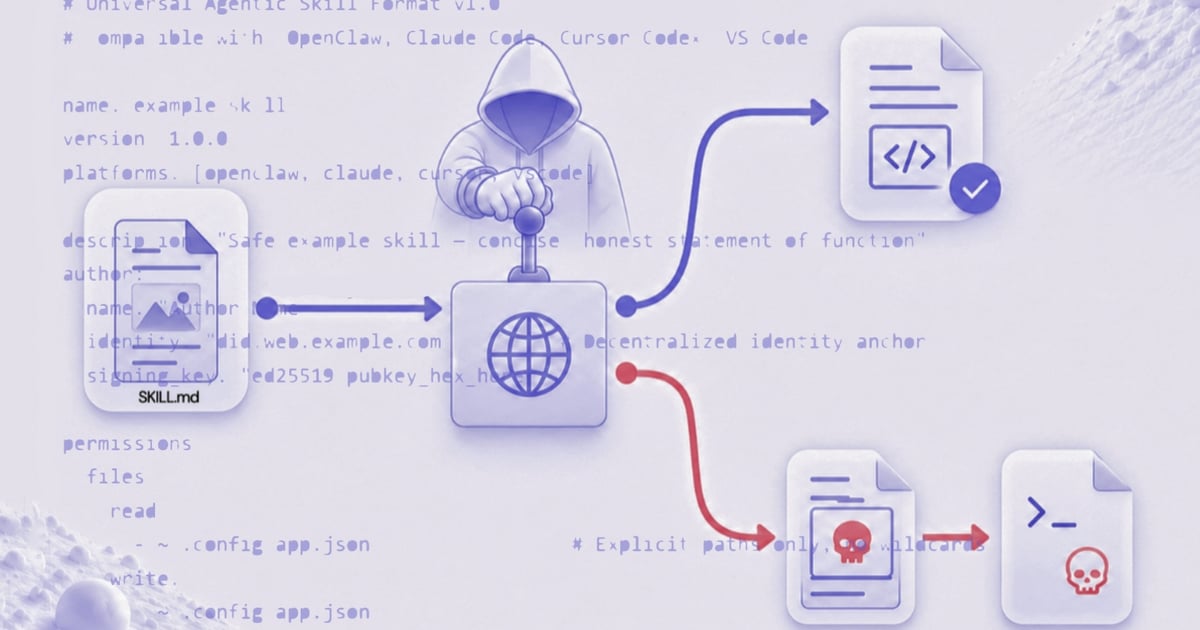
OWASP AI skill risks blueprint flags seven concrete skill‑related risks that threaten cloud workloads, with actionable mitigation steps for DevOps teams.

Trend Micro researchers detail an npm supply chain attack RedC2 that drops an AI‑enabled Linux backdoor, exposing Node.js ecosystems to advanced command‑and‑con