

LiteLLM Master Key Leak Enables GitHub Token Theft and Release Pipeline Hijack
A leaked LiteLLM master key exposed a GitHub OAuth token, enabling attackers to steal organization tokens and publish malicious releases.
12 stories
A leaked LiteLLM master key exposed a GitHub OAuth token, enabling attackers to steal organization tokens and publish malicious releases.
OVHcloud’s GitHub account was accessed by actors linked to the GlassWorm threat group, resulting in credential theft and malicious code injection into private.

GhostAction injected malicious GitHub Actions workflows into over 34,000 repositories, exfiltrating secrets via plain HTTP to a hard-coded IP.
Analyze the AgentCorruption vulnerability in AWS Bedrock AgentCore, detailing the single-prompt attack path, permissions obtained, and cloud audit logs.
Google reveals its PageBreak internal AI agent discovered over 500 cross-site scripting vulnerabilities across corporate web applications using deterministic.

An unpatched LMCache vulnerability leaves AI inference servers vulnerable to unauthenticated remote code execution via insecure Python deserialization.
A detailed guide on SASE framework deployment, showing how organizations can build a Secure Access Service Edge framework to protect edge computing and remote.

A new Linux kernel vulnerability gives ARM64 KVM guests read-write access to host memory, allowing them to escape and run code on the host machine.
Enterprise AI agents are generating uncontrolled compute spend, prompting urgent cost-control measures and new governance frameworks.
Comprehensive engineering checklist for auditing cloud-native Kubernetes clusters. Hardening runtime eBPF telemetry, Falco rules, RBAC least privilege, and network policies.
City Hall launches a cyber defense effort, seeking external experts to patch legacy systems, harden cloud workloads, and meet emerging compliance mandates.
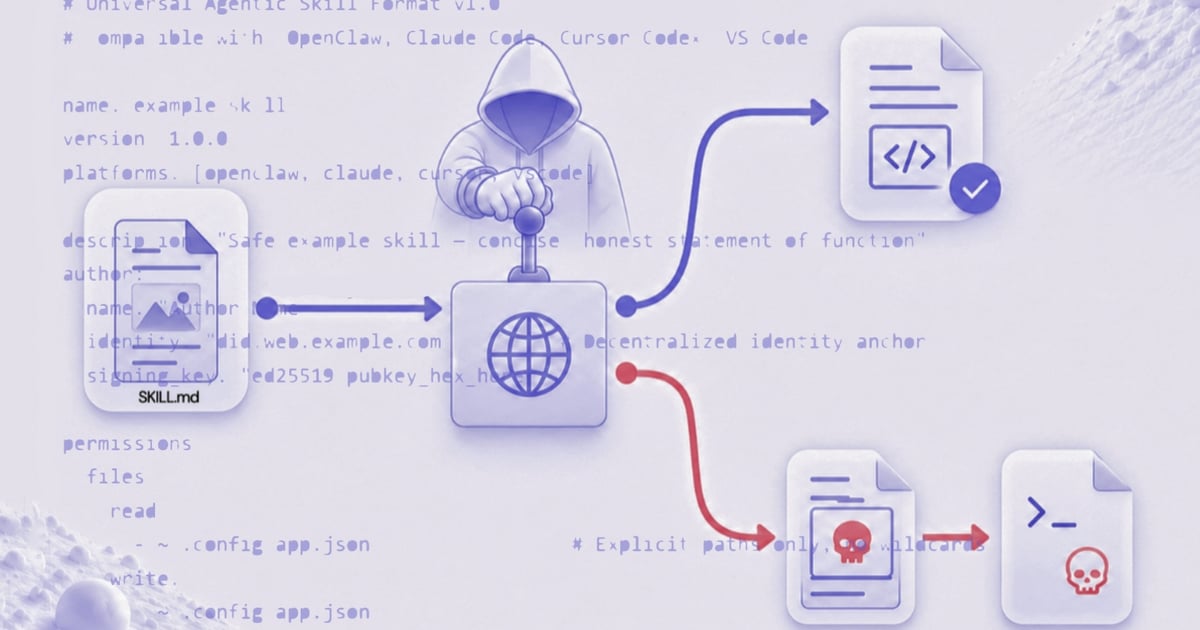
OWASP AI skill risks blueprint flags seven concrete skill‑related risks that threaten cloud workloads, with actionable mitigation steps for DevOps teams.