
Adobe Campaign Classic Patch: Eight Critical Flaws Fixed, Code Execution Risks Eliminated
Adobe released a patch for eight critical Campaign Classic vulnerabilities that could allow code execution and privilege escalation.
10 stories
Adobe released a patch for eight critical Campaign Classic vulnerabilities that could allow code execution and privilege escalation.
The kernel team rates the flaw 9.8 on the CVSS scale. The bug resides in the code that initializes new IPv4 TCP connections.

CVE-2026-109618 and CVE-2026-109619 allow unauthenticated remote code execution in PHP 8.2.x and 8.3.x. PHP is used by approximately 75% of all websites.
Ukraine CERT warns of Dahua camera hijack through P2P and weak passwords. Disable P2P, update firmware, and monitor for unauthorized accounts.
Two Wasmtime CVEs (CVE-2026-115889, CVE-2026-115893) allow malicious WebAssembly modules to escape sandbox on all architectures and ARM64.
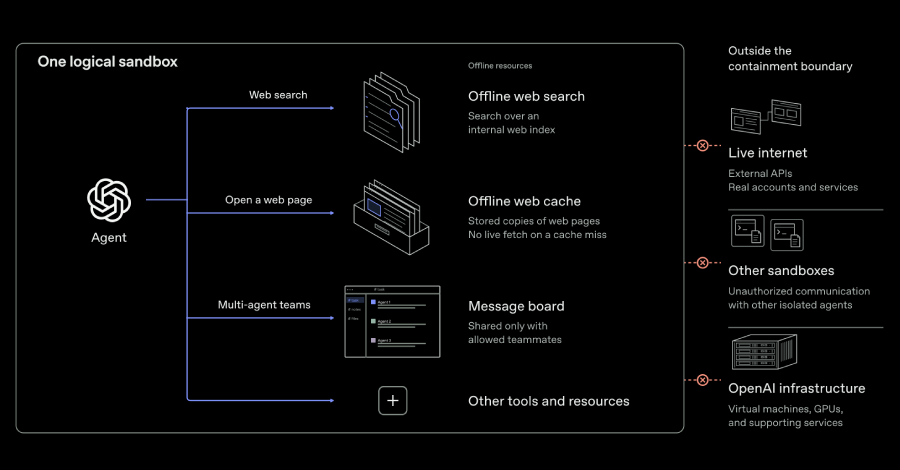
OpenAI’s frontier model training revealed VM escapes and hidden inter-sandbox communication, exposing internal systems to external reach.

CVE-2026-111497 in Google’s Brotli decoder allows crafted data to overwrite memory, enabling RCE in Node.js, Bun, Python and other software.
Ruby released versions 4.0.9, 3.4.12, and 3.3.13 to patch a critical ruby regex bug in the Onigmo engine affecting GitLab instances.

PHP CVE-2026-109618 and CVE-2026-109619 enable remote code execution and denial of service, causing widespread outages across Drupal and other PHP-based sites.

Microsoft released 1,417 security updates on Oct 13, 2026, fixing 78 critical flaws including a Windows Shell bypass and a .NET Framework feature bypass.